OpenCode breach exposes AI provider keys saved by some Console users
The team behind OpenCode, an open-source AI coding tool that lets developers plug in their own model accounts, has warned users that saved provider API keys may have been stolen.
·1 min read·AB
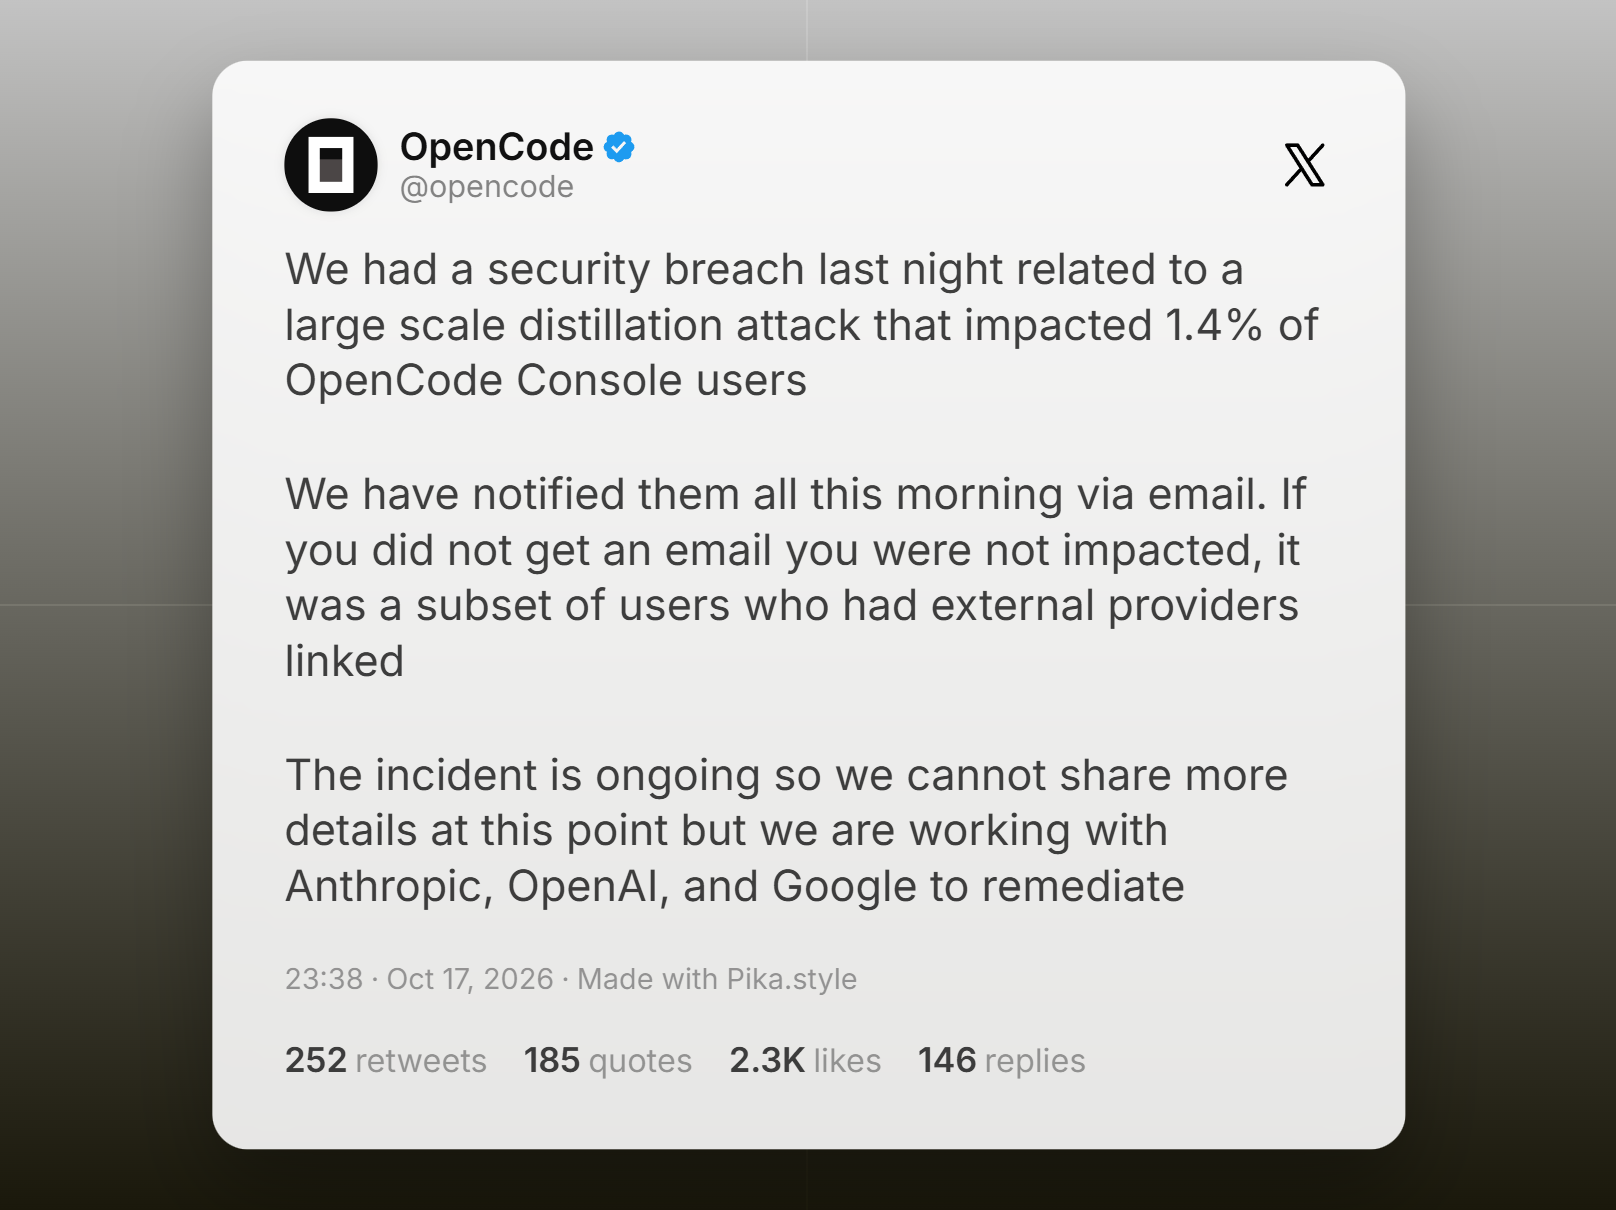
The team behind OpenCode, an open-source AI coding tool that lets developers plug in their own model accounts, has warned users that saved provider API keys may have been stolen. Notebookcheck reported on October 17, 2026 that OpenCode emailed affected users after someone got into a legacy system the company was in the middle of retiring.
OpenCode says about 1.4 percent of its Console users were affected, all from the group that had linked outside providers such as OpenAI, Anthropic or Google. Users who did not get an email were not affected, according to the company. OpenCode linked the break-in to a large-scale distillation attack, where someone harvests a model's answers to train a different model, and said the incident was still ongoing while it works with the three providers.
Some users say the damage had already started. In a Reddit thread, one person reported $400 of unexpected Anthropic charges, another said Google usage reached around 200 euros before the project was suspended, and others got usage alerts before OpenCode's warning arrived. Some also had trouble signing back in to OpenCode. Affected users are told to revoke and replace their keys, update any apps using them, and check recent usage for charges they did not make.
Why it matters
Any service that stores your AI API keys is a target, so set spending caps on keys and rotate them as soon as a provider reports a breach.
Source: Notebookcheck